An agent reaching across many apps on the user's behalf accumulates access no one can see, because per-prompt dialogs leave no durable record of what it can touch.
← Back to patterns
Google
Memory, Context & Boundary
EmergingConsent
See and Control What Your Agent Can Touch
Per-prompt "allow this?" dialogs train the reflex click and leave no record of what the agent can reach. Where a knowledge-source toggle scopes a single query, this is the durable layer above it: one surface listing every app the agent can touch right now — with scope, grantor, and expiry — where any grant can be inspected, narrowed, extended, or revoked inline.
Metaphor
Permissions Pane
Interaction
Grant, Revoke, Inspect
Use case
Multi-tool agents, Connector management, Granting & revoking access
Failure mode
Modal-as-Consent
Control mechanisms
Permission Cards · Scope Sliders · Expiry Dates · Periodic Review Prompts
Reference examples
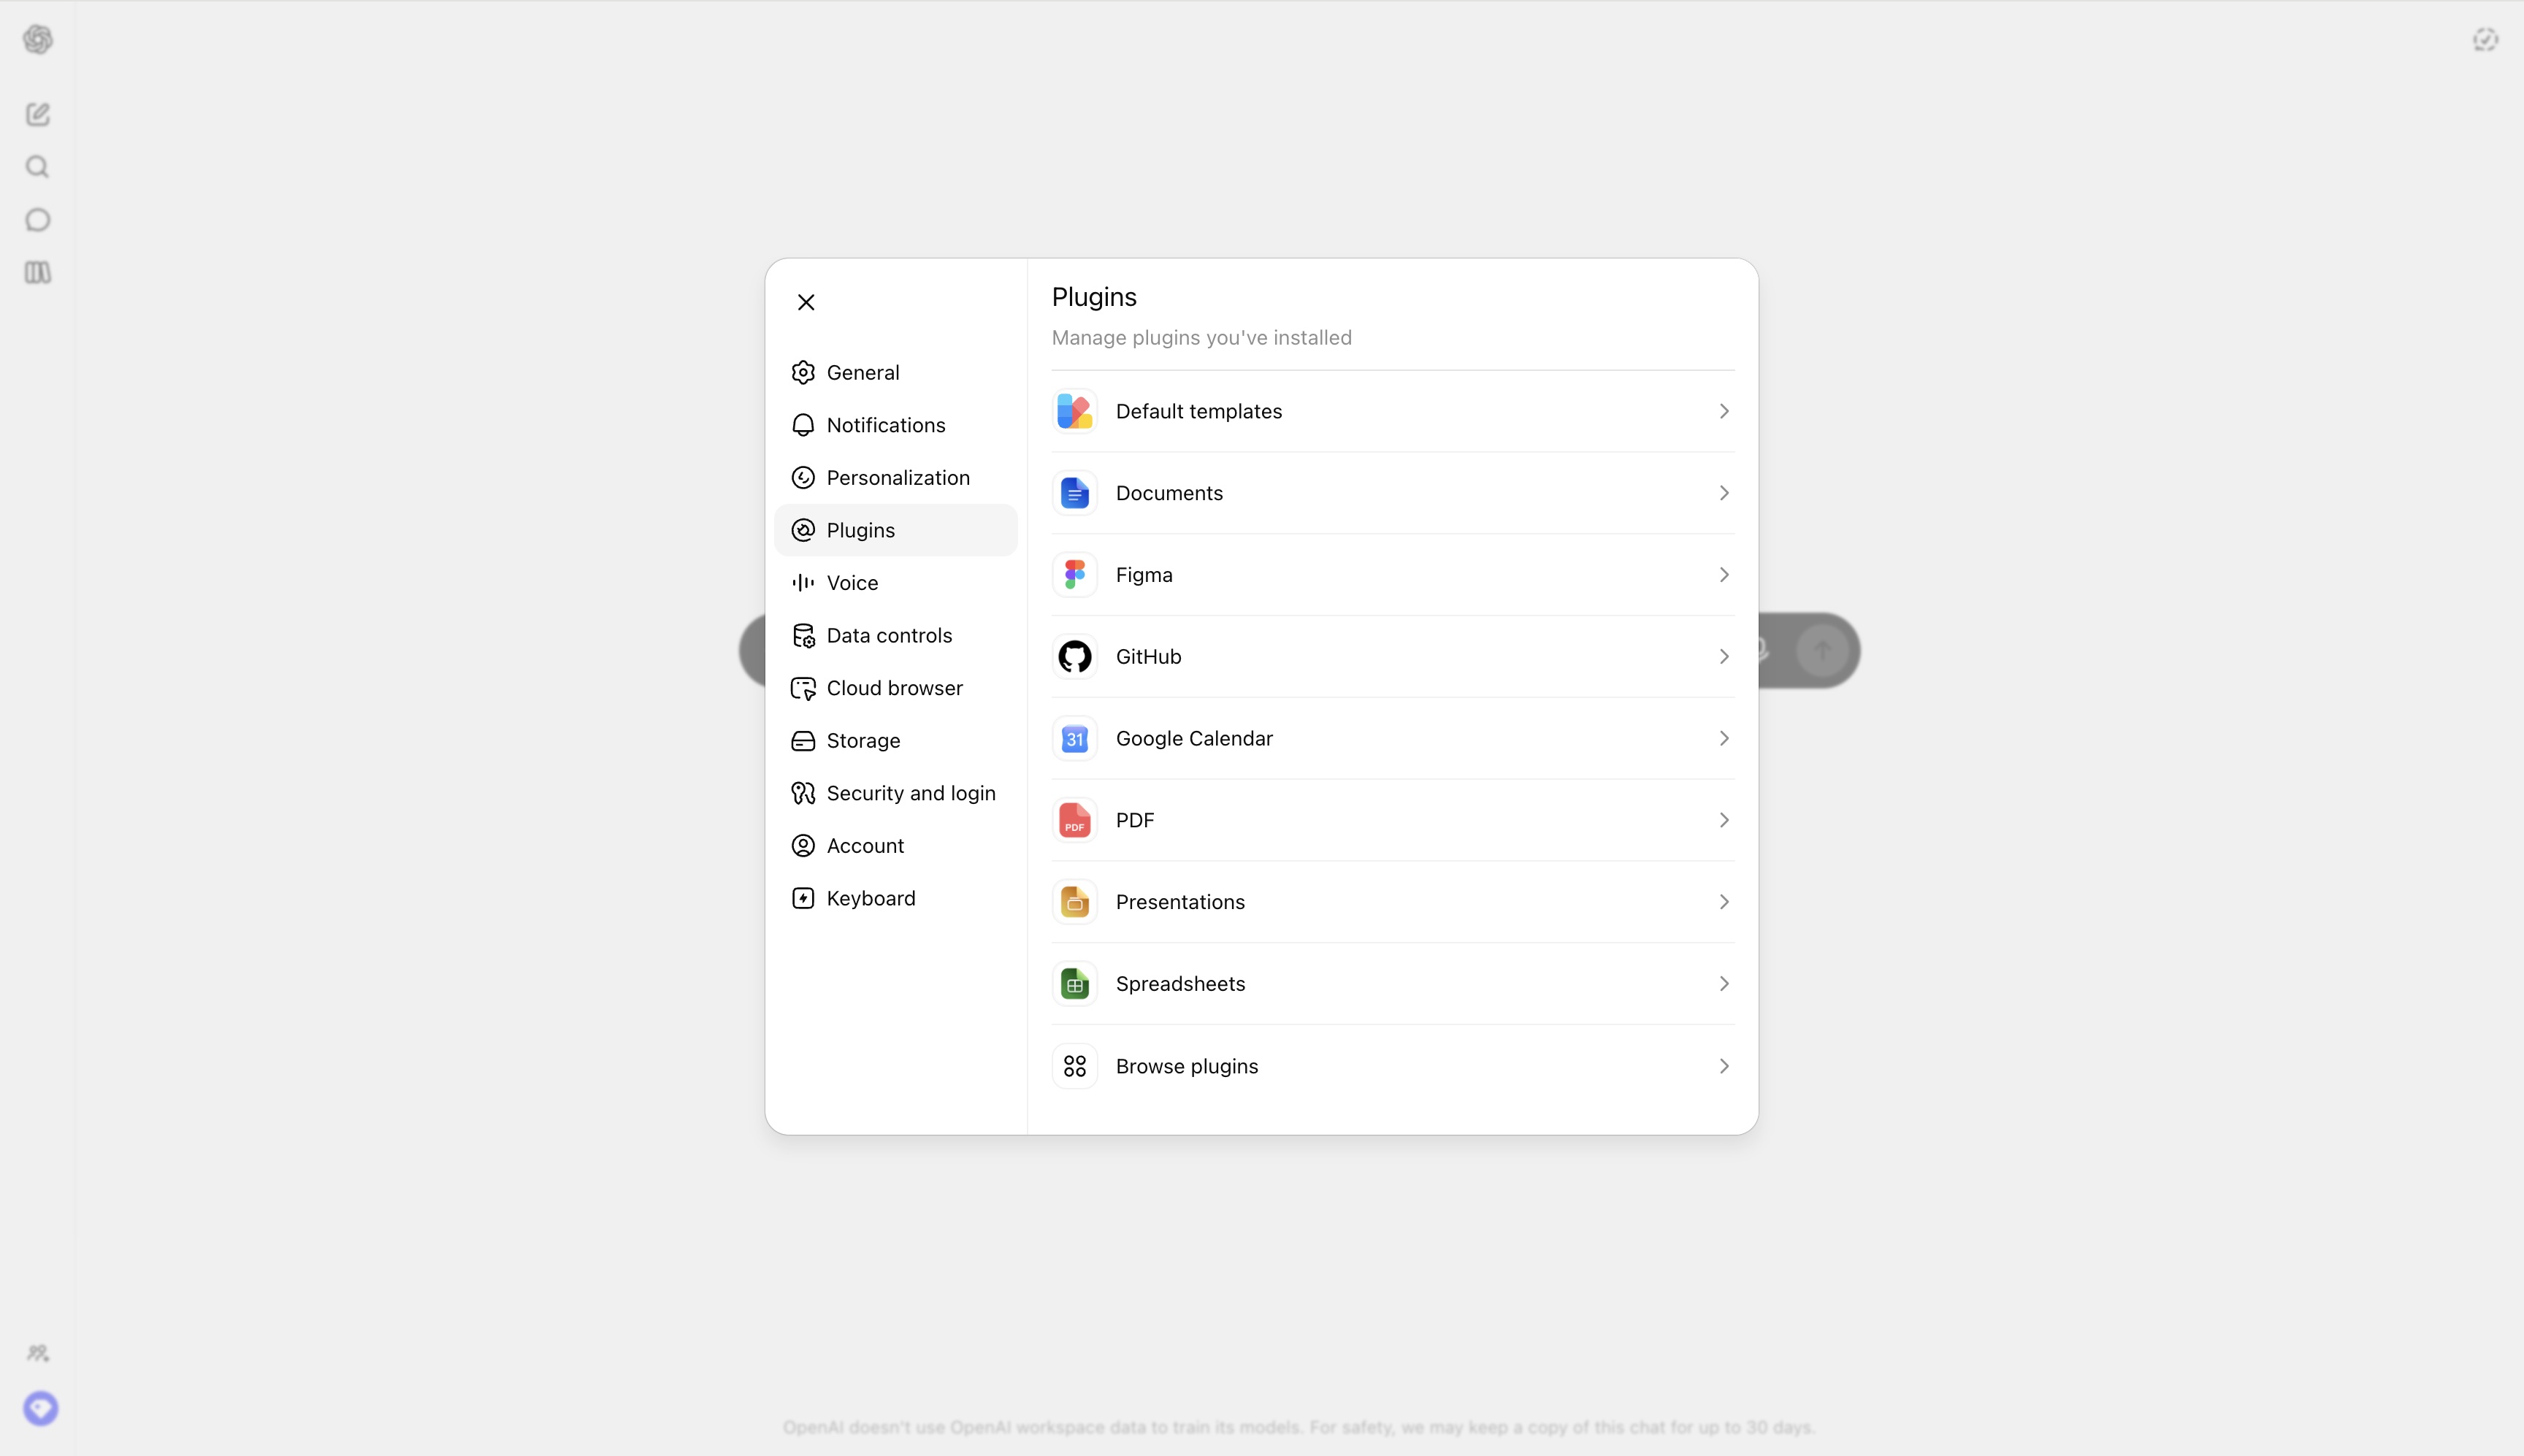
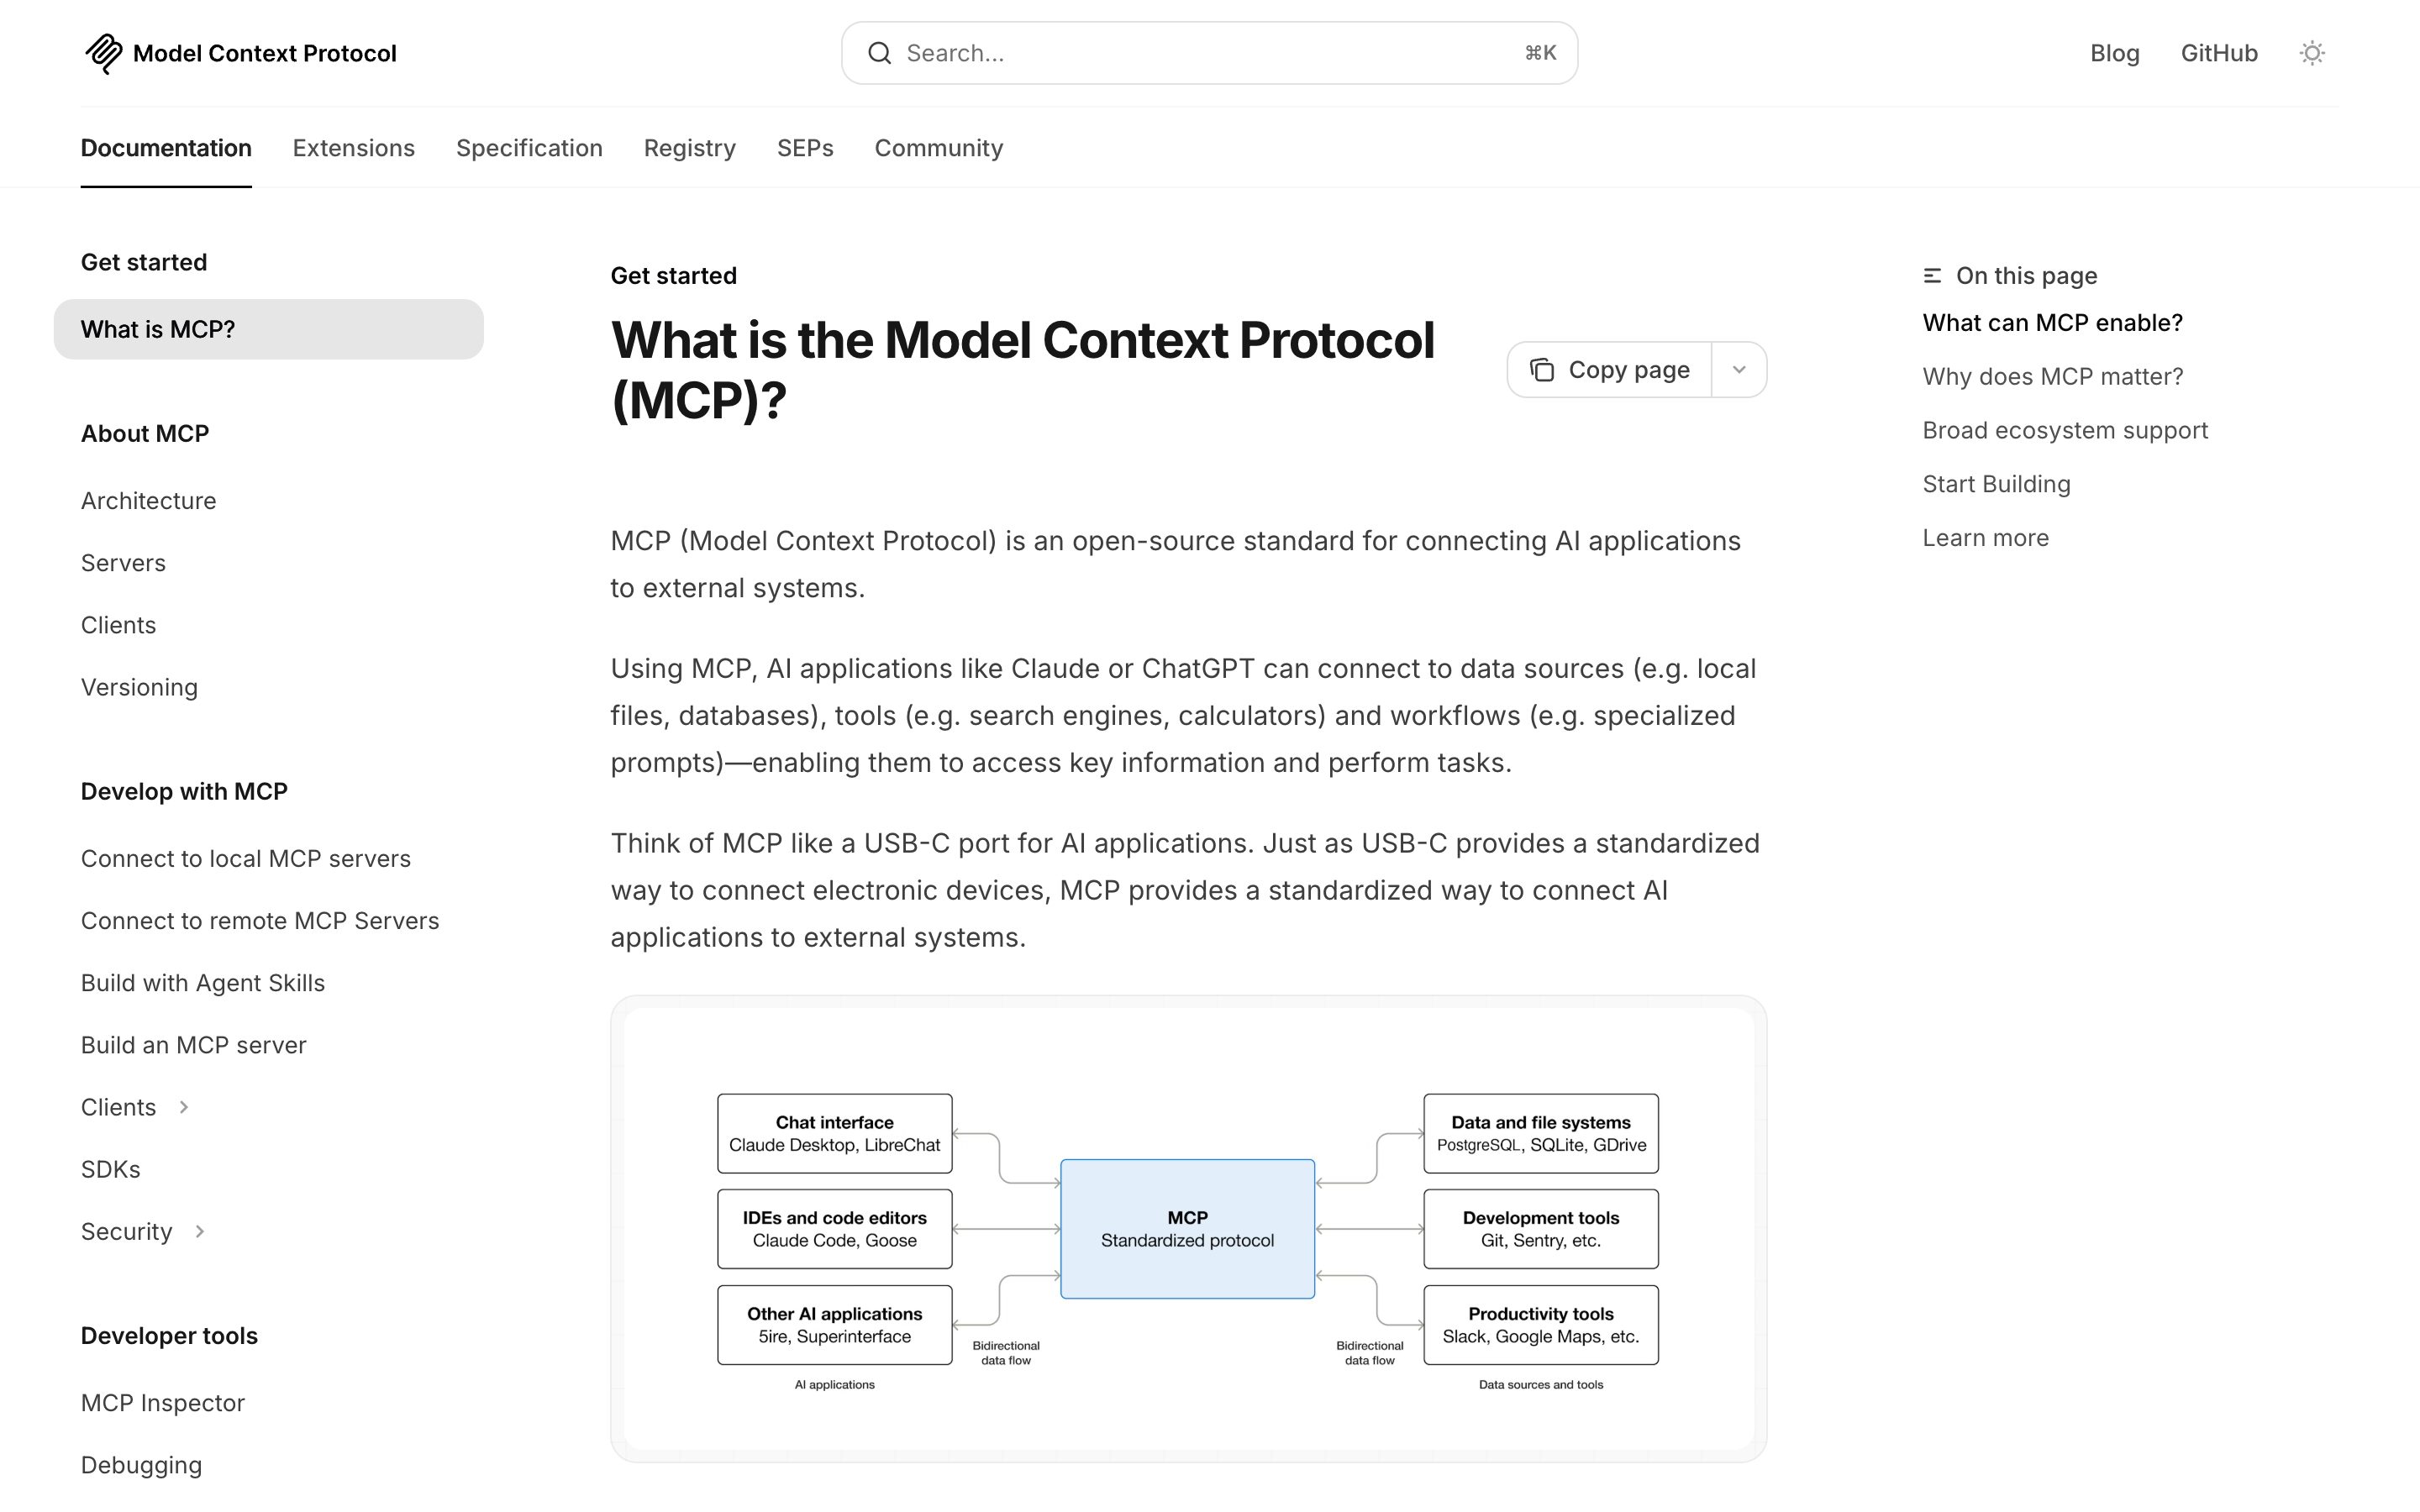
Auth0 Fine-Grained Authorization · Google Workspace third-party app access · OpenAI ChatGPT Connectors · Anthropic Claude MCP server consent
Interactive Example
The live side-by-side is the comparison.
This prototype already contains the contrast between chat and the pattern response. It stands as the primary comparison surface for this page.
A permission you typed in chat dies with the chat.
Agents reach across calendars, inboxes, and files on your behalf, but a per-query toggle grants trust in a way that cannot be revoked, audited, or refreshed later. Permission issued mid-conversation evaporates with the session, leaving access that is neither visible nor accountable — trust by vibes, not by record.
Consent lifts permission out of the transcript and into a dedicated surface where each grant is a first-class artifact: scoped, time-bound, and revocable on a single pane. You can see every active grant with its grantor and expiry, narrow or extend it, and review it on a cadence — so durable access stays inspectable instead of accumulating in the dark.
"Permissions you can list, scope, and revoke are infrastructure; permissions buried in chat history are a liability."
DOPE Lens
How this pattern improves AI interaction quality.
Observability
Every active permission is visible on a single surface with scope, grantor, expiry
Directability
Revoke, narrow, extend, or re-bind any grant at any time
Predictability
Scope and expiry are explicit — there is no implicit grant the user has not seen
Explainability
Each permission lists exactly what data and actions it covers, in plain language
Fit
Where it earns its place.
Use it
when
when
A standing, revocable map of what the agent can reach beats a stream of one-off "allow this?" prompts that vanish the moment they are clicked.
Avoid
when
when
The agent reaches a single trusted system within one fixed scope, where a standing permission surface adds chrome with nothing to control.
In the wild
Where this pattern already ships.
The pattern is shipping but still maturing across products. Entries below show how different teams have approached it; expect variation as the space settles.
Auth0 · Fine-Grained Authorization
Okta
Relationship-based access control aimed at AI agents: durable grants with explicit scope, expiry, and inspectable history. Permissions as inspectable artifacts, not modal choices.
Visit Okta ↗
Google Workspace · third-party app access
Per-app, per-scope, per-user permission panels in the Admin console. Revocation propagates immediately; expiry policies and review prompts at the workspace level.
Visit Google ↗
OpenAI ChatGPT · Connectors
OpenAI
Settings → Connectors lists every linked service with the scopes granted and a per-connector revoke. The cleanest consumer-facing implementation of "every grant is visible on one surface."
Visit OpenAI ↗
Anthropic Claude · MCP server consent
Anthropic
Each MCP server connection is a durable grant with a visible scope description; tool calls show the granting server inline. Mid-maturity — UI varies across surfaces (desktop, Claude Code) and the org-wide audit view is not yet unified.
Visit Anthropic ↗
Research Frame
Why this pattern exists, and where it breaks.
Render every grant on one inspectable surface — which app, what scope, granted by whom, expiring when — sitting above the per-query toggle, and let the user narrow, extend, or revoke any of it inline.
Permissions approved in chat die with the session and cannot be seen, audited, or revoked later, so the agent's reach only ever grows.
Without a review cadence the surface still drifts — grants accumulate, scopes broaden, and a permission list no one revisits becomes its own blind spot.
Common questions
What people ask about this pattern.
When should I use the Consent pattern?
+
A standing, revocable map of what the agent can reach beats a stream of one-off "allow this?" prompts that vanish the moment they are clicked.
When should I avoid the Consent pattern?
+
The agent reaches a single trusted system within one fixed scope, where a standing permission surface adds chrome with nothing to control.
What problem does Consent solve?
+
An agent reaching across many apps on the user's behalf accumulates access no one can see, because per-prompt dialogs leave no durable record of what it can touch.
Why is chat the wrong fit for this?
+
Permissions approved in chat die with the session and cannot be seen, audited, or revoked later, so the agent's reach only ever grows.
Related Patterns
Curated connections, not just neighbors.
Hand-picked relationships — what this pattern pairs with in practice, what it replaces, what it builds on, and what builds on it.
Often paired with
Autonomy Dial
Autonomy Dial sets which tools run freely, ask first, or stay off; Consent sets which apps the agent can reach and for how long.
Often paired with
Data Ownership
Consent controls what the agent can still reach; Data Ownership lists what it has collected, ready to export or delete.
Extends
Knowledge Source Toggle
Knowledge Source Toggle scopes one query; Consent is the durable permission layer above it, across sessions and revocable.